What Is Pixel Tracking? How Tracking Pixels Work, and When You Need Consent
Pixel tracking explained: how a tracking pixel sends data, Meta, TikTok and email pixels, pixel vs cookie, consent, blocking, installing and testing.
Article summary
TL;DR
Pixel tracking records what people do on a website or in an email by making their browser or mail app call a server. The call comes from a tiny image (often 1×1) or a JavaScript tag, and carries the page, the time, device details and an identifier. Ad platforms such as Meta, TikTok and Google use it to count conversions.
- A tracking pixel is a request, not a picture: loading it sends the page, time, IP address, browser and an identifier to the pixel's server.
- Today most pixels are JavaScript tags (Meta Pixel, TikTok Pixel, Google tag). The 1×1 image survives mostly in email.
- In the EU, the EDPB says Article 5(3) of the ePrivacy Directive covers tracking pixels: non-essential ones need consent before they fire.
- In the US, the FTC acted against GoodRx and BetterHelp in 2023 for sharing health data through advertising tools. Health-adjacent brands should map what their pixels send.
- Send Purchase after the payment succeeds, from your server as well as the browser, with one shared event ID so it isn't counted twice.
 ChatGPT
 Claude
 Perplexity
 Grok
On this page
Pixel tracking is how a website, an ad or an email finds out what you did with it. A tiny piece of content makes your browser or mail app call a server, and the call itself is the data. Merchants rely on it to count sales from Meta, TikTok and Google ads. Readers meet it in every marketing email they open. This guide covers both sides: how it works, what it sends, where the law draws lines, how to block it, and how a store should install and test it. By industry: server-side tracking for supplement brands, server-side tracking for skincare brands, server-side tracking for online pharmacies, server-side tracking for telehealth companies, server-side tracking for fitness brands and server-side tracking for info product businesses.
What is pixel tracking?
Pixel tracking is a way to record an action (a page view, an email open, a purchase) by having the visitor's software request a resource from a tracking server. The resource is called a tracking pixel, web beacon, pixel tag or clear GIF.
The name comes from the original form: an image of 1×1 pixel, transparent, that nobody sees. The European Data Protection Board gives the cleanest definition:
A tracking pixel is a hyperlink to a resource, usually an image file, embedded into a piece of content like a website or an email. This pixel usually fulfils no purpose related to the requested content itself; its sole purpose is to automatically establish a communication by the client to the host of the pixel.
The image is now the exception. The FTC notes that tracking pixels "have evolved from tiny, pixel-sized images on web pages" to "a broad range of HTML and JavaScript embedded in web sites (and email)".3FTC Office of Technology, Lurking Beneath the Surface: Hidden Impacts of Pixel Tracking, March 16, 2023 The Meta Pixel, for instance, is "a snippet of JavaScript code that allows you to track visitor activity on your website".7Meta for Developers, Meta Pixel It still ends the same way: a request to a server.
How does a tracking pixel work?
Take an email or a product page with a pixel in it. Four things happen in less than a second.
Fig. 1What happens when a pixel loads
approved declined or closed routing step
- Page or email opensContains the pixel's code or image
- loadsBrowser requests the pixelURL carries event, page, IDs
- sendsPixel server logs itAdds IP, time, browser, cookies
- processesEvent in the reportMatched to a campaign or profileApproved
the request is the data
Nothing is "downloaded" in a meaningful sense: the server answers with a blank image or nothing at all. What matters is what traveled with the request. Here is what a simplified pixel call looks like, with the data written into the URL:
GET https://pixel.example.com/track?ev=Purchase&value=59.00¤cy=USD&order=10482&id=PIXEL_ID Referer: https://yourstore.com/checkout/thank-you User-Agent: Mozilla/5.0 (iPhone; CPU iPhone OS 18_0 like Mac OS X) ... Cookie: visitor_id=fb.1.1728900000.123456789
Three parts carry information. The URL parameters say what happened (a purchase of $59). The headers say where and on what device (the page, the browser, and the IP address, which the server sees on every connection). The cookie says who, as far as the platform can tell: an identifier set on an earlier visit. The EDPB describes it the same way: pixels "may also contain additional identifiers, metadata or content as part of the link", added by the site owner or generated by the pixel's JavaScript.1EDPB, Guidelines 2/2023 on Technical Scope of Art. 5(3) of ePrivacy Directive, version 2.0, adopted October 7, 2024
Types of tracking pixels
Every pixel works the same way. What differs is who runs it and what it's for.
| Type | Examples | What it records | Who receives the data |
|---|---|---|---|
| Ad platform pixel | Meta Pixel, TikTok Pixel, Google tag | Page views, add to cart, checkout, purchase | The ad platform, to measure ads and build audiences |
| Conversion pixel | The ad pixel's Purchase or Lead event on the confirmation page | One completed action and its value | The ad platform, to credit a campaign |
| Retargeting pixel | Same ad pixels, used for audiences | Who viewed a product without buying | The ad platform, to show ads again |
| Analytics pixel | Google Analytics through the Google tag | Sessions, pages, funnels | Your analytics tool |
| Email open pixel | Your email tool's 1×1 image | Whether and when the email was opened | Your email service provider |
| Affiliate pixel | A network's tag on your thank-you page | Which partner sent the sale | The affiliate network, to pay commission |
The three ad pixels most stores install describe themselves plainly. TikTok: "a piece of code that you can place on your website that allows you to share website events with TikTok".11TikTok Ads Manager Help, About TikTok Pixel Google: "a single tag you can add to your website" that sends data "to linked Google product destinations", such as Google Ads and Google Analytics.13Google Tag Manager Help, About the Google tag The distinction that matters legally is first party versus third party: a pixel that only feeds your own analytics is different from one that sends visitor data to an ad network.
What data does a tracking pixel send?
Meta's documentation is one of the few that lists what a pixel collects. It names five categories.7Meta for Developers, Meta Pixel
Fig. 2One Purchase event, as an ad platform receives it
- HTTP headers
- IP address, browser, page URL, referrer
- Pixel data
- Pixel ID and the platform's first-party cookie
- Button clicks
- Buttons clicked and their labels
- Optional values
- value 59.00 · currency USD · content IDs
- Form field names
- email, address, quantity (names, not what was typed)
- Advanced matching
- Hashed email or phone, only if you turn it on
Illustrative record.
most of it comes for free with the request
The last line is where most of the risk sits. Meta says field values aren't captured unless the site sends them through Advanced Matching or custom data.7Meta for Developers, Meta Pixel Hashing doesn't make that data anonymous: the FTC points out that hashes "can be reversed or used to link data across different databases".3FTC Office of Technology, Lurking Beneath the Surface: Hidden Impacts of Pixel Tracking, March 16, 2023 And a pixel on a page sends the page URL. If the URL or the product name reveals something sensitive, that goes too.
Tracking pixel vs cookie vs server-side tracking
The three are often confused because they work together.
| Tracking pixel | Cookie | Server-side tracking | |
|---|---|---|---|
| What it is | A request from the browser or mail app to a server | A small file stored in the browser | A request from your server to the platform's API |
| Where it runs | Visitor's browser or email client | Visitor's browser | Your backend, or a server you control |
| What it does | Sends an event | Remembers an identifier between visits | Sends an event, often confirmed by your own systems |
| Stopped by ad blockers | Often | Can be deleted or capped | Out of reach: the browser isn't involved |
| Needs consent in the EU | Consent first, unless strictly necessary | Consent first, unless strictly necessary | The same rules apply to the data you send |
| Examples | Meta Pixel, TikTok Pixel, email open pixel | Meta's _fbp, Google's _ga | Meta Conversions API, TikTok Events API |
A pixel usually reads or sets a cookie, which is how a platform knows that today's purchase and last week's ad click came from the same browser. Server-side tracking moves the sending from the browser to your server: the platform receives the event from you, after your systems confirm it. It's more reliable, and it doesn't change the consent question. We cover how it works and how to set it up in server-side tracking for ecommerce.
Email tracking pixels and Apple Mail Privacy Protection
Email is where the 1×1 image is still the norm. The EDPB puts it simply: "the sender may include a tracking pixel to detect when the receiver reads the email".1EDPB, Guidelines 2/2023 on Technical Scope of Art. 5(3) of ePrivacy Directive, version 2.0, adopted October 7, 2024 Each recipient gets a unique image URL, so when the image loads, the email tool marks that person as having opened.
Two mail apps changed what that signal means.
Fig. 3The same email, two mail settings
Images load on open
- Email arrivesPixel not loaded yet
- laterReader opens itMail app loads the image
- requestsSender's serverLogs an open, with the IP
The sender learns when you read it, on what device, from which IP
Apple Mail, Protect Mail Activity on
- Email arrivesApple downloads remote content in the background
- requestsSender's serverLogs a load, IP hidden
- laterReader opens it, or notNo new request
An open is logged whether or not the person reads it
the open you count may not be a person
Apple says that with Protect Mail Activity, "your IP address is hidden from senders" and "remote content is privately downloaded in the background when you receive a message (instead of when you view it)".14Apple Support, Protect email privacy in Mail on Mac Gmail scans images before showing them and says senders can't use image loading to learn about your computer or location. It also says "sometimes, senders may know whether you've opened an email that has an image".15Gmail Help, Choose whether to show images
For a store, the takeaway is practical: open rates overstate reading among Apple Mail users. Judge email flows on clicks and orders, and don't use "opened" alone to decide who gets a win-back or a sunset email.
Inside Tagada
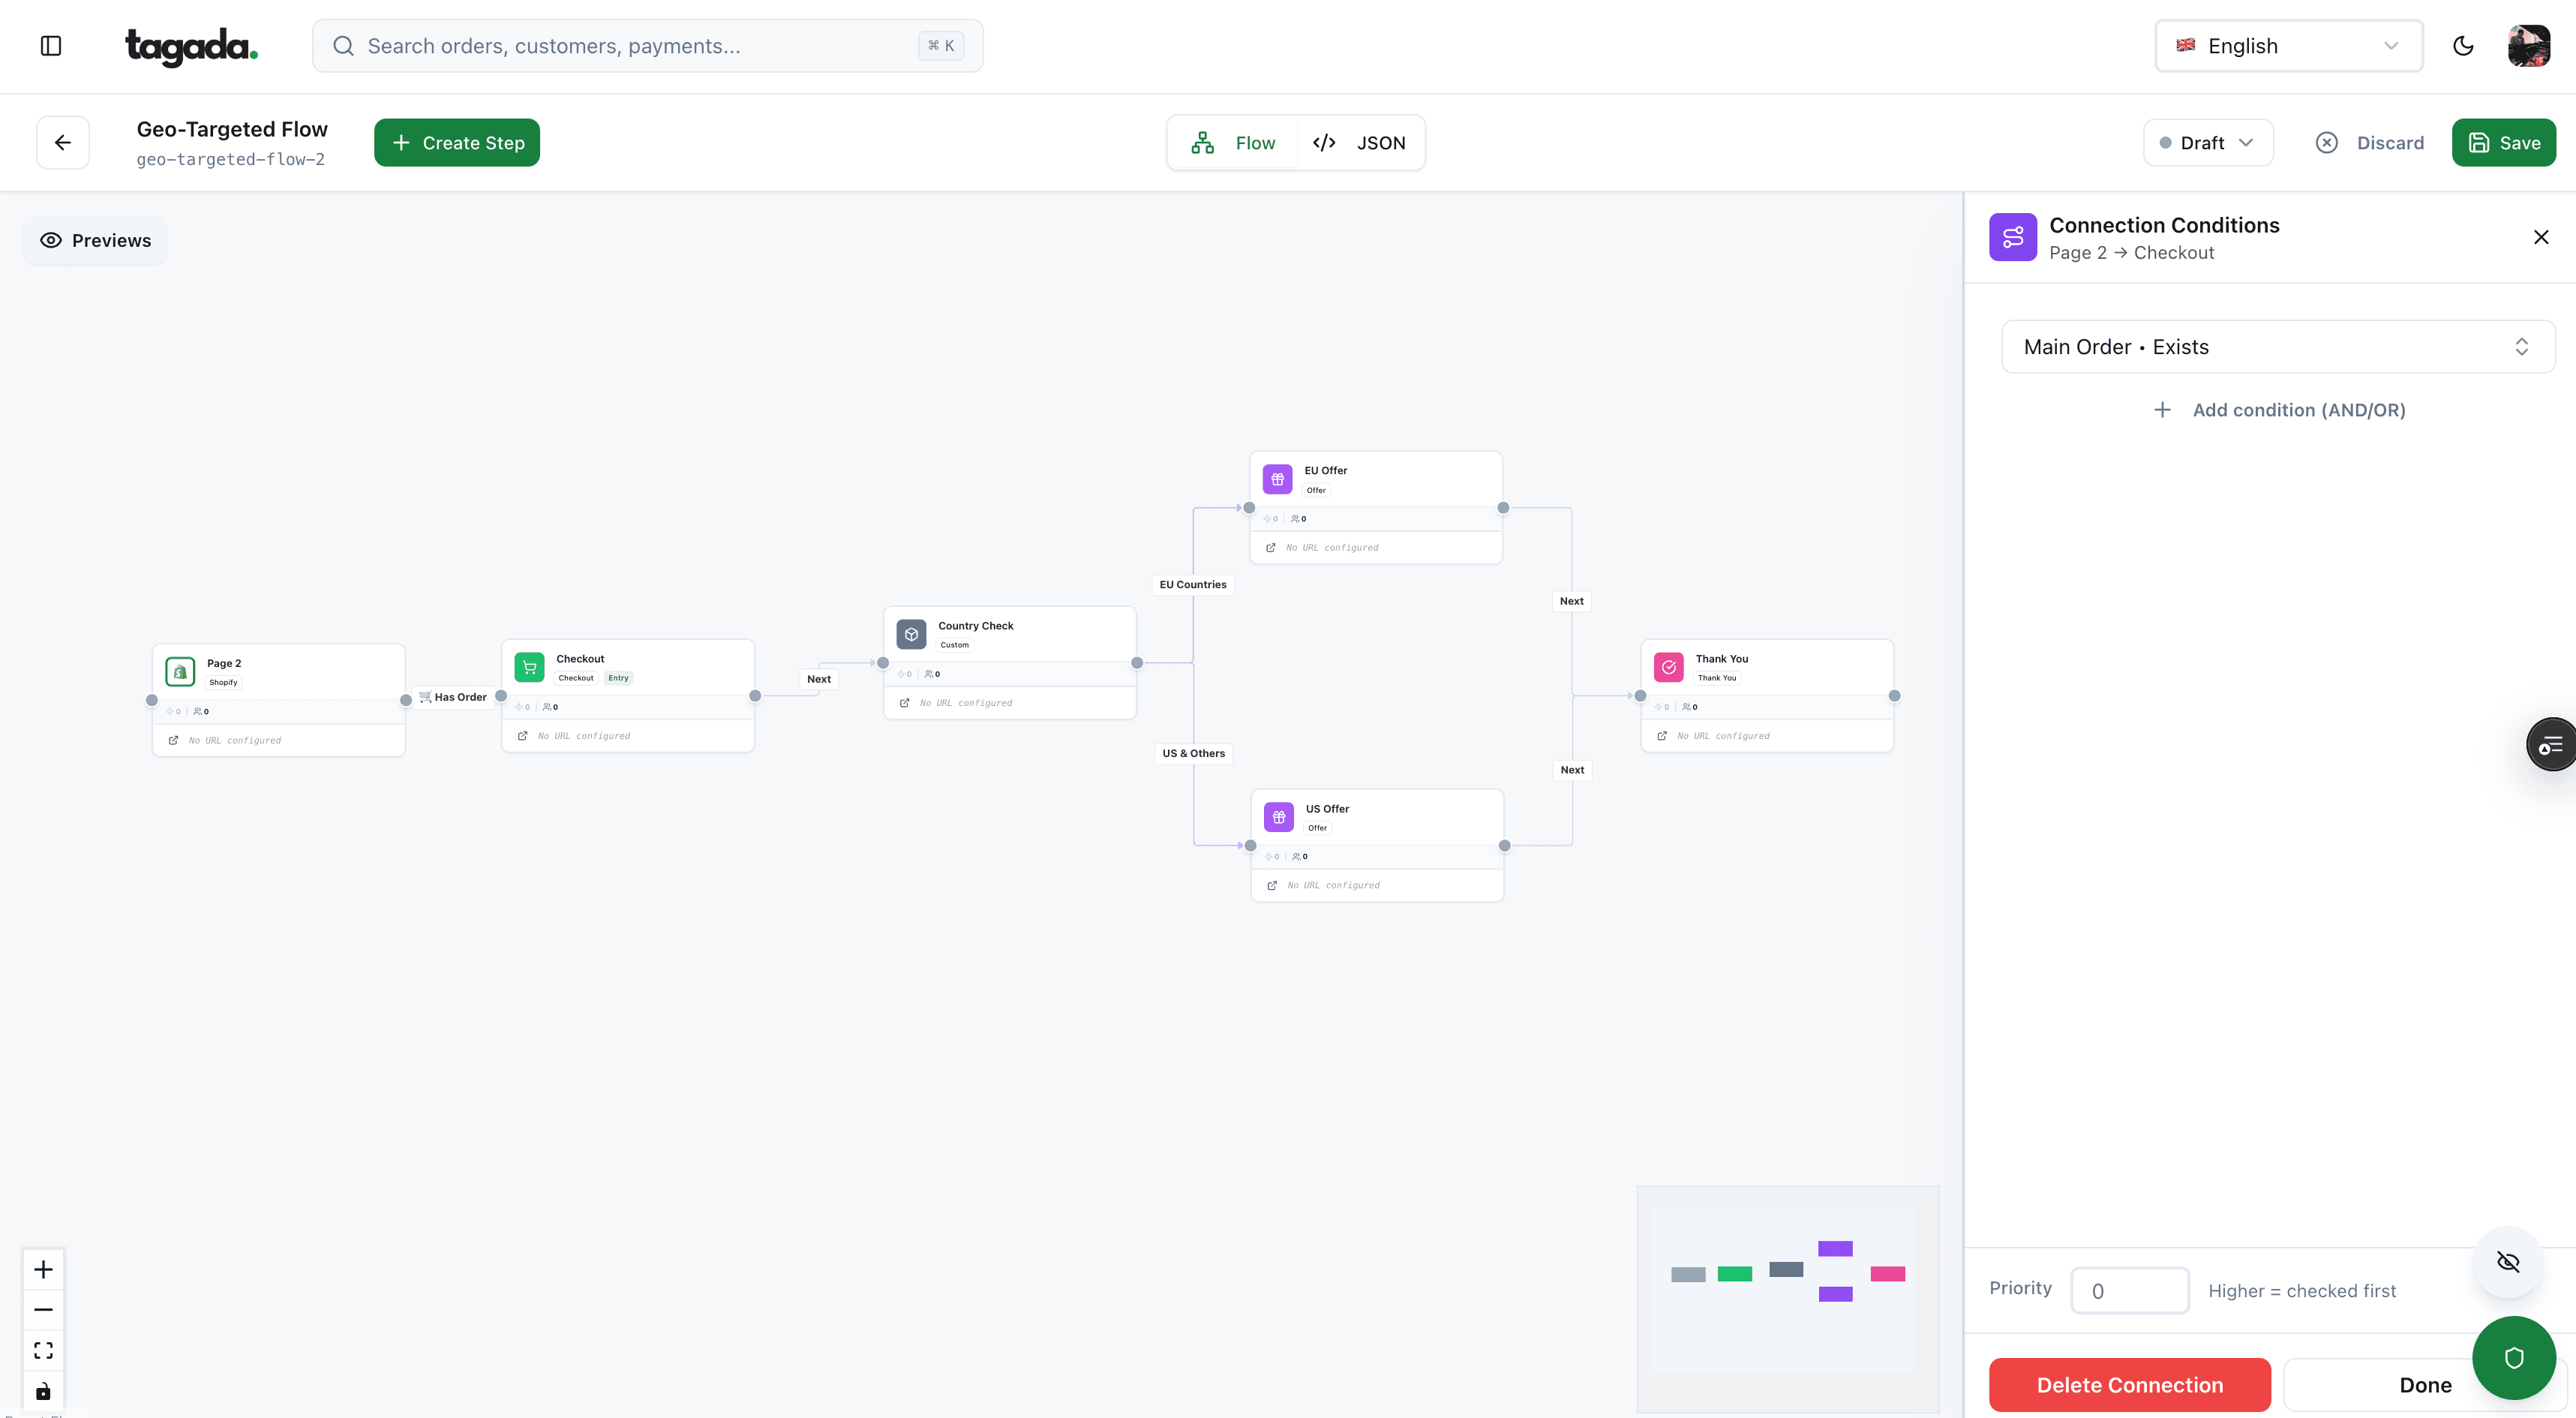
Build the funnel once, route every customer to the right offer
Checkout, upsells and subscriptions on one flow, with conditions per country, order or customer.
Why pixels miss events
A pixel only counts what reaches the server. Several things stand between the visitor and that server, and none of them shows up as an error in your ad dashboard.
- Visitor uses an ad blocker or privacy extensionThe request to the pixel's domain is blocked: no eventSend key events server-side as well
- Visitor uses SafariCross-site cookies are blocked, and script-written storage is deleted after seven days of Safari use without interaction with the siteExpect weaker matching to old ad clicks
- Visitor refuses consent (EU, UK)A compliant setup doesn't fire marketing pixelsRespect it; measure with consented and modeled data
- Buyer pays, then closes the tab before the thank-you pageThe Purchase event in the browser never firesTrigger Purchase from the payment confirmation
- Pixel installed twice (theme code and an app)Every purchase counts doubleKeep one installation; test with the platform's tools
The Safari behavior comes from WebKit's Intelligent Tracking Prevention: since March 2020, "cookies for cross-site resources are now blocked by default across the board", and a website's script-writable storage is deleted "after seven days of Safari use without user interaction on the site".16WebKit, Full Third-Party Cookie Blocking and More, March 24, 2020 You'll see vendor percentages for how much data each of these costs. None comes from a measurement of your store, so treat them as marketing until you compare pixel purchases with your own order count.
Is pixel tracking legal?
Pixel tracking is legal. What's regulated is when it fires, what it sends and who receives it. The rules differ sharply between the EU and the US.
In the EU and UK: consent before the pixel fires
Article 5(3) of the ePrivacy Directive allows storing or reading information on a user's device only with the user's consent, after clear information about the purposes. Two exceptions apply: storage needed for the transmission of a communication, and storage "strictly necessary" to provide a service the user explicitly asked for.2Directive 2002/58/EC (ePrivacy Directive), consolidated text, Article 5(3) It's the rule behind cookie banners.
For years, some argued that pixels escaped it because they don't store a cookie themselves. The EDPB closed that debate in its Guidelines 2/2023 (final version adopted October 7, 2024). Sending a tracking pixel to a device "does constitute storage, at the very least through the caching mechanism of the client-side software", so Article 5(3) "is applicable, even if this storage is not permanent". And for JavaScript pixels, the collection of identifiers counts as "gaining of access".1EDPB, Guidelines 2/2023 on Technical Scope of Art. 5(3) of ePrivacy Directive, version 2.0, adopted October 7, 2024 The guidelines cover email pixels too.
In practice: ad and analytics pixels that aren't strictly necessary must wait for consent from EU visitors. Shopify builds this in: in markets that require consent, usually the EEA and UK, "web pixels run only when visitors have provided the permissions required in the pixel configuration", and new pixels require Marketing and Analytics permissions by default.17Shopify Help Center, Pixels overview
In the US: no general consent rule, but enforcement on sensitive data
The US has no federal equivalent of Article 5(3). The FTC has acted on what pixels share, especially health data.
Fig. 4US actions on tracking pixels and health data
- Feb 2023 · GoodRxFirst FTC action under the Health Breach Notification Rule; $1.5M civil penalty
- Mar 2023 · BetterHelpProposed order: $7.8M for consumer refunds, ban on sharing health data for ads
- Mar 2023 · FTCOffice of Technology post on hidden impacts of pixel tracking
- Jun 20, 2024 · CourtPart of the HHS bulletin on tracking technologies vacated (AHA v. Becerra)
- Jun 26, 2024 · HHS OCRBulletin for HIPAA entities, last reviewed with a note on the order
read them if you sell anything health-adjacent
- GoodRx (February 2023). The FTC said GoodRx shared users' prescription medications and health conditions with Facebook, Google, Criteo and others, despite promising not to. The proposed order included a $1.5 million civil penalty and would permanently ban it from sharing health information for advertising.4FTC, FTC Enforcement Action to Bar GoodRx from Sharing Consumers' Sensitive Health Info for Advertising, February 1, 2023
- BetterHelp (March 2023). The FTC said BetterHelp passed email addresses, IP addresses and health questionnaire answers to Facebook, Snapchat, Criteo and Pinterest for advertising. The proposed order would require $7.8 million for consumer refunds and banned sharing health data for ads.5FTC, FTC to Ban BetterHelp from Revealing Consumers' Data, Including Sensitive Mental Health Information, to Facebook and Others for Targeted Advertising, March 2, 2023
- The FTC's warning. Its Office of Technology wrote that pixels "can track and send all sorts of personal data", including "specific items a user has purchased" or "information users have typed within a form", and that improper sharing can fall under the FTC Act and the Health Breach Notification Rule.3FTC Office of Technology, Lurking Beneath the Surface: Hidden Impacts of Pixel Tracking, March 16, 2023
- HHS guidance for HIPAA entities. HHS's Office for Civil Rights names "web beacons or tracking pixels" among the tracking technologies its bulletin covers. It says a cookie banner is not a valid HIPAA authorization, and that a tracking vendor receiving protected health information needs a business associate agreement. On June 20, 2024, a federal court in Texas vacated the part of the guidance that treated an IP address plus a visit to a public page about a health condition as covered.6HHS Office for Civil Rights, Use of Online Tracking Technologies by HIPAA Covered Entities and Business Associates (last reviewed June 26, 2024) Whether your payment processor also needs a BAA: HIPAA and payment processors.
HIPAA applies to health plans, providers and their business associates, not to most online stores. The FTC's Health Breach Notification Rule and the FTC Act reach further. Shopify also stops pixels configured as data sale for customers who opted out of the sale or sharing of their data, which matters under US state privacy laws.17Shopify Help Center, Pixels overview
Health-adjacent brands
If you sell supplements, wellness or other health-related products, check what your pixels send: product names in URLs, quiz answers, form fields, Advanced Matching. The FTC cases were about health information reaching ad platforms, not about pixels as such. Get legal advice for your own setup.
How to block tracking pixels
For readers who want to stop being tracked, most of the work is in the mail app and the browser.
| Where | Setting | What it does |
|---|---|---|
| Gmail (web) | Settings › See all settings › Images › Ask before displaying external images | Images, including pixels, load only when you click "Display images below"15Gmail Help, Choose whether to show images |
| Apple Mail | Settings › Privacy › Protect Mail Activity | Hides your IP and loads remote content in the background on arrival14Apple Support, Protect email privacy in Mail on Mac |
| Apple Mail | Turn off Protect Mail Activity, then Block All Remote Content | Nothing loads until you choose to download it14Apple Support, Protect email privacy in Mail on Mac |
| Safari | Intelligent Tracking Prevention, on by default | Blocks cross-site cookies; pixels still fire but match less16WebKit, Full Third-Party Cookie Blocking and More, March 24, 2020 |
| Any browser | Content blocker or ad-blocking extension | Blocks requests to known tracking domains |
| Websites in the EU and UK | Reject marketing or analytics cookies in the banner | A compliant site doesn't fire those pixels |
Plain-text email and refusing images are the only ways to be sure an email pixel never loads. In a browser, blockers work on lists of known domains, so a pixel served from the site's own domain or sent server-side won't be caught.
How to install a tracking pixel on Shopify
Shopify manages pixels in one place, Settings › Customer events. Pixels there are "JavaScript code snippets that run on your online store, customer accounts pages, or store checkout".17Shopify Help Center, Pixels overview
- Use the platform's app first. For Meta, Shopify recommends the Facebook & Instagram channel; for Google, the Google & YouTube channel.21Shopify Help Center, Migrating pixels
- Add a custom pixel only if no app pixel meets your needs. In Customer events, add a custom pixel and paste the platform's code. It runs in a "Lax sandbox", so some functions may not work, and Shopify says compliance and troubleshooting are your responsibility.18Shopify Help Center, Custom pixels
- Set the permissions. Choose which customer permissions the pixel needs (Marketing, Analytics) and whether it counts as data sale. This decides when it runs.17Shopify Help Center, Pixels overview
- Subscribe to standard events. Shopify publishes events such as
page_viewed,product_viewed,product_added_to_cart,checkout_started,payment_info_submittedandcheckout_completed, which "logs when a visitor completes a purchase".19Shopify Dev Docs, Web Pixels API standard events - Remove the old copies. Pixels pasted in the theme, in checkout.liquid (Shopify Plus) or in the checkout's Additional scripts should be migrated, or every event fires twice.21Shopify Help Center, Migrating pixels
Sources: Shopify Help Center, Pixels overview, Custom pixels and Migrating pixels.
On other platforms the logic is the same: one installation per pixel, through the platform's integration when there is one, with consent wired in before launch.
How to test a pixel
Never trust a pixel you haven't watched fire. Four checks cover most failures.
Browser check
Meta Ads Data Advisor (formerly Meta Pixel Helper) is a free Chrome extension. It shows how many Pixel events fired on the page and reports errors.9Meta for Developers, Meta Ads Data Advisor (formerly Meta Pixel Helper)
Platform check
In Meta Events Manager › Data Sources › your Pixel › Test Events, browser and server events appear live. Server events need the test_event_code, removed in production.10Meta for Developers, Conversions API: Using the API (Test Events)
Consent check
Reject cookies in a private window, then browse and buy. No marketing event should fire. Accept, repeat, and the events should appear.
Order check
Over a week, compare Purchase events with real paid orders. Twice as many means a duplicate; far fewer means blocked or missing events.
Fire Purchase after the payment, not before
The Purchase event drives ad bidding, so it has to mean money received. Two mistakes are common. Firing it on the click of the Pay button counts declined cards and abandoned 3D Secure checks as sales. Firing it only from the thank-you page misses buyers who pay and never load it. Stripe warns that you "can't rely on triggering fulfillment only from your checkout landing page, because it's not guaranteed customers visit that page".20Stripe Docs, Fulfill orders (Checkout Sessions) The payment confirmation, usually a webhook, is the reliable moment. The sequence is explained in our checkout flow guide.
Fig. 5One confirmed payment, several destinations
 MetaBrowser Pixel + Conversions API, same event and event ID
 TikTokBrowser Pixel + Events API, same event and event_id
 GoogleGoogle tag, plus server-side tagging if you use it
- Your order recordSource of truth for revenue and refunds
one event ID for every copy
Sending the same event from the browser and the server is what Meta recommends, and deduplication makes it safe. Meta matches the Pixel's eventID with the Conversions API's event_id and the event names, and discards the later copy when both arrive within 48 hours.8Meta for Developers, Handling Duplicate Pixel and Conversions API Events TikTok works the same way: share the event_id through the Pixel and the Events API, and identical events arriving within 48 hours are deduplicated.12TikTok Ads Manager Help, Event deduplication
Practical rule
Create the event ID once, when the checkout or the order is created, and store it on the order. Both the browser and the server read it from there. An ID generated again after a 3D Secure redirect, or a different one per payment processor, turns one sale into two.
For subscriptions, each successful renewal is its own charge and needs its own event ID. Failed retries send nothing. How renewals are charged is covered in subscription payment processing, and how to credit sales across channels in attribution modeling.
Tracking with Tagada
How Tagada helps
Server-side tracking from the checkout
Tagada sends events server-side to Meta, Google and TikTok, from the same platform that runs the checkout. The checkout handles order bumps, one-click upsells, Apple Pay and Google Pay, and subscriptions with retries. Tagada runs standalone or with Shopify, WooCommerce or a headless store. See pricing for plans.
Frequently asked questions
What is a tracking pixel?
Is pixel tracking legal?
How do I know if an email has a tracking pixel?
Is a tracking pixel the same as a cookie?
Do I need the Conversions API if I have the Meta Pixel?
What is pixel rank tracking?
Sources
Checked October 14, 2026- EDPB, Guidelines 2/2023 on Technical Scope of Art. 5(3) of ePrivacy Directive, version 2.0, adopted October 7, 2024
- Directive 2002/58/EC (ePrivacy Directive), consolidated text, Article 5(3)
- FTC Office of Technology, Lurking Beneath the Surface: Hidden Impacts of Pixel Tracking, March 16, 2023
- FTC, FTC Enforcement Action to Bar GoodRx from Sharing Consumers' Sensitive Health Info for Advertising, February 1, 2023
- FTC, FTC to Ban BetterHelp from Revealing Consumers' Data, Including Sensitive Mental Health Information, to Facebook and Others for Targeted Advertising, March 2, 2023
- HHS Office for Civil Rights, Use of Online Tracking Technologies by HIPAA Covered Entities and Business Associates (last reviewed June 26, 2024)
- Meta for Developers, Meta Pixel
- Meta for Developers, Handling Duplicate Pixel and Conversions API Events
- Meta for Developers, Meta Ads Data Advisor (formerly Meta Pixel Helper)
- Meta for Developers, Conversions API: Using the API (Test Events)
- TikTok Ads Manager Help, About TikTok Pixel
- TikTok Ads Manager Help, Event deduplication
- Google Tag Manager Help, About the Google tag
- Apple Support, Protect email privacy in Mail on Mac
- Gmail Help, Choose whether to show images
- WebKit, Full Third-Party Cookie Blocking and More, March 24, 2020
- Shopify Help Center, Pixels overview
- Shopify Help Center, Custom pixels
- Shopify Dev Docs, Web Pixels API standard events
- Stripe Docs, Fulfill orders (Checkout Sessions)
- Shopify Help Center, Migrating pixels
Tagada
Server-side events to Meta, Google and TikTok, from the checkout
Funnels, one-click upsells, subscription billing and payment routing, on one customer record.
- 01Create your free account
- 02Connect your store or build a checkout
- 03Launch funnels, upsells and subscriptions