What Is CAVV in a Card Payment?
CAVV meaning: the 3-D Secure value from the issuer. Where it travels, CAVV vs CVV, AAV and ECI, what invalid CAVV result codes mean, and liability shift.
Article summary
TL;DR
CAVV (Cardholder Authentication Verification Value) is the value a Visa card issuer returns after 3-D Secure authenticates the cardholder, or records an attempt. The merchant sends it in the authorization request and the issuer verifies it. With ECI 5 or 6, it blocks most fraud disputes against the merchant. Mastercard's equivalent is the AAV.
- CAVV stands for Cardholder Authentication Verification Value. It is created by the issuer's 3-D Secure server, not printed on the card.
- It travels in the authorization request. Visa only allows ECI 5 or 6 when the CAVV was included.
- CVV2 proves the card details. CAVV proves the cardholder passed 3-D Secure for this one payment.
- An invalid CAVV result means the issuer could not verify the value. That payment gets no fraud liability shift.
- A CAVV is single-use: Visa treats reuse on a different transaction as a compliance case, and forbids storing it after authorization.
 ChatGPT
 Claude
 Perplexity
 Grok
On this page
CAVV is the receipt of a 3-D Secure check. When a customer pays online with a Visa card and the issuer runs 3-D Secure, the issuer hands back a short value that says "we authenticated this cardholder, for this payment." That value is the CAVV. The merchant forwards it with the payment, and it decides who pays if the transaction later turns out to be fraud.
What is CAVV?
CAVV stands for Cardholder Authentication Verification Value. Visa's rules define it as "a unique value transmitted in response to an Authentication Request."1Visa Core Rules and Visa Product and Service Rules, April 18, 2026 Three facts matter for a merchant:
- Who creates it. The issuer's Access Control Server (ACS), the bank's 3-D Secure server. Every issuer in Visa Secure must include a CAVV in its authentication confirmations and attempt responses. If the issuer doesn't support Visa Secure, Visa answers for it with an attempt response that also carries a CAVV.1Visa Core Rules and Visa Product and Service Rules, April 18, 2026
- What it looks like. 20 bytes, Base64-encoded into a 28-character string, for example
CJSJbzXT6TRQlvZDX+ZdOG4QriE=(Stripe's test value).3Stripe API reference, Create a PaymentIntent (three_d_secure)4Stripe Docs, Import 3D Secure results Adyen accepts 20 or 21 bytes.5Adyen Docs, Standalone 3D Secure authentication - What it proves. That the issuer authenticated the cardholder, or recorded an attempt, for this specific transaction. EMV 3-D Secure calls it the authentication value; Stripe lists AAV, CAVV and AEVV as names for the same field.3Stripe API reference, Create a PaymentIntent (three_d_secure)
How CAVV works, from checkout to authorization
- Checkout. The customer enters a Visa card. Your 3DS server sends an authentication request to Visa's directory server, which forwards it to the issuer's ACS.
- Authentication. The ACS approves silently (frictionless) or asks the customer for a code, an app approval or biometrics.
- Result. The ACS returns a status (
transStatusY for authenticated, A for attempted), an ECI and the CAVV.3Stripe API reference, Create a PaymentIntent (three_d_secure) - Authorization. Your processor puts the CAVV, the ECI and the 3DS transaction ID in the authorization request. At Adyen,
authenticationValuegoes intompiData.cavv.5Adyen Docs, Standalone 3D Secure authentication - Verification. The issuer, or Visa on its behalf, checks the CAVV and returns a CAVV result code with the authorization response. If no one verifies it, Visa's rules say the CAVV "is assumed to be valid."1Visa Core Rules and Visa Product and Service Rules, April 18, 2026
The CAVV is created during authentication and checked during authorization, two separate steps.
For the full 3-D Secure flow, exemptions and SCA rules, see our guide to payment authentication.
Example: one order, one CAVV
Fig. 1What a 3-D Secure result looks like
- transStatus
- Y · authenticated
- ECI
- 05
- CAVV
- CJSJbzXT…QriE= · 28 characters
- 3DS transaction ID
- aaa65c7b-… · a UUID
- CAVV result in authorization
- 2 · passed validation
Illustrative record.
the CAVV is one field among several
Two months later the cardholder reports the $80 charge as fraud. Under Visa's rules, a dispute under condition 10.4 (Other Fraud, Card-Absent) is invalid when the authorization carried ECI 5 and a CAVV from a Visa Secure EMV 3DS authentication confirmation.1Visa Core Rules and Visa Product and Service Rules, April 18, 2026 The fraud loss stays with the issuer. Had the merchant added $9 of shipping after 3-D Secure and reused the same CAVV on an $89 authorization, the value would no longer match the payment it was created for.
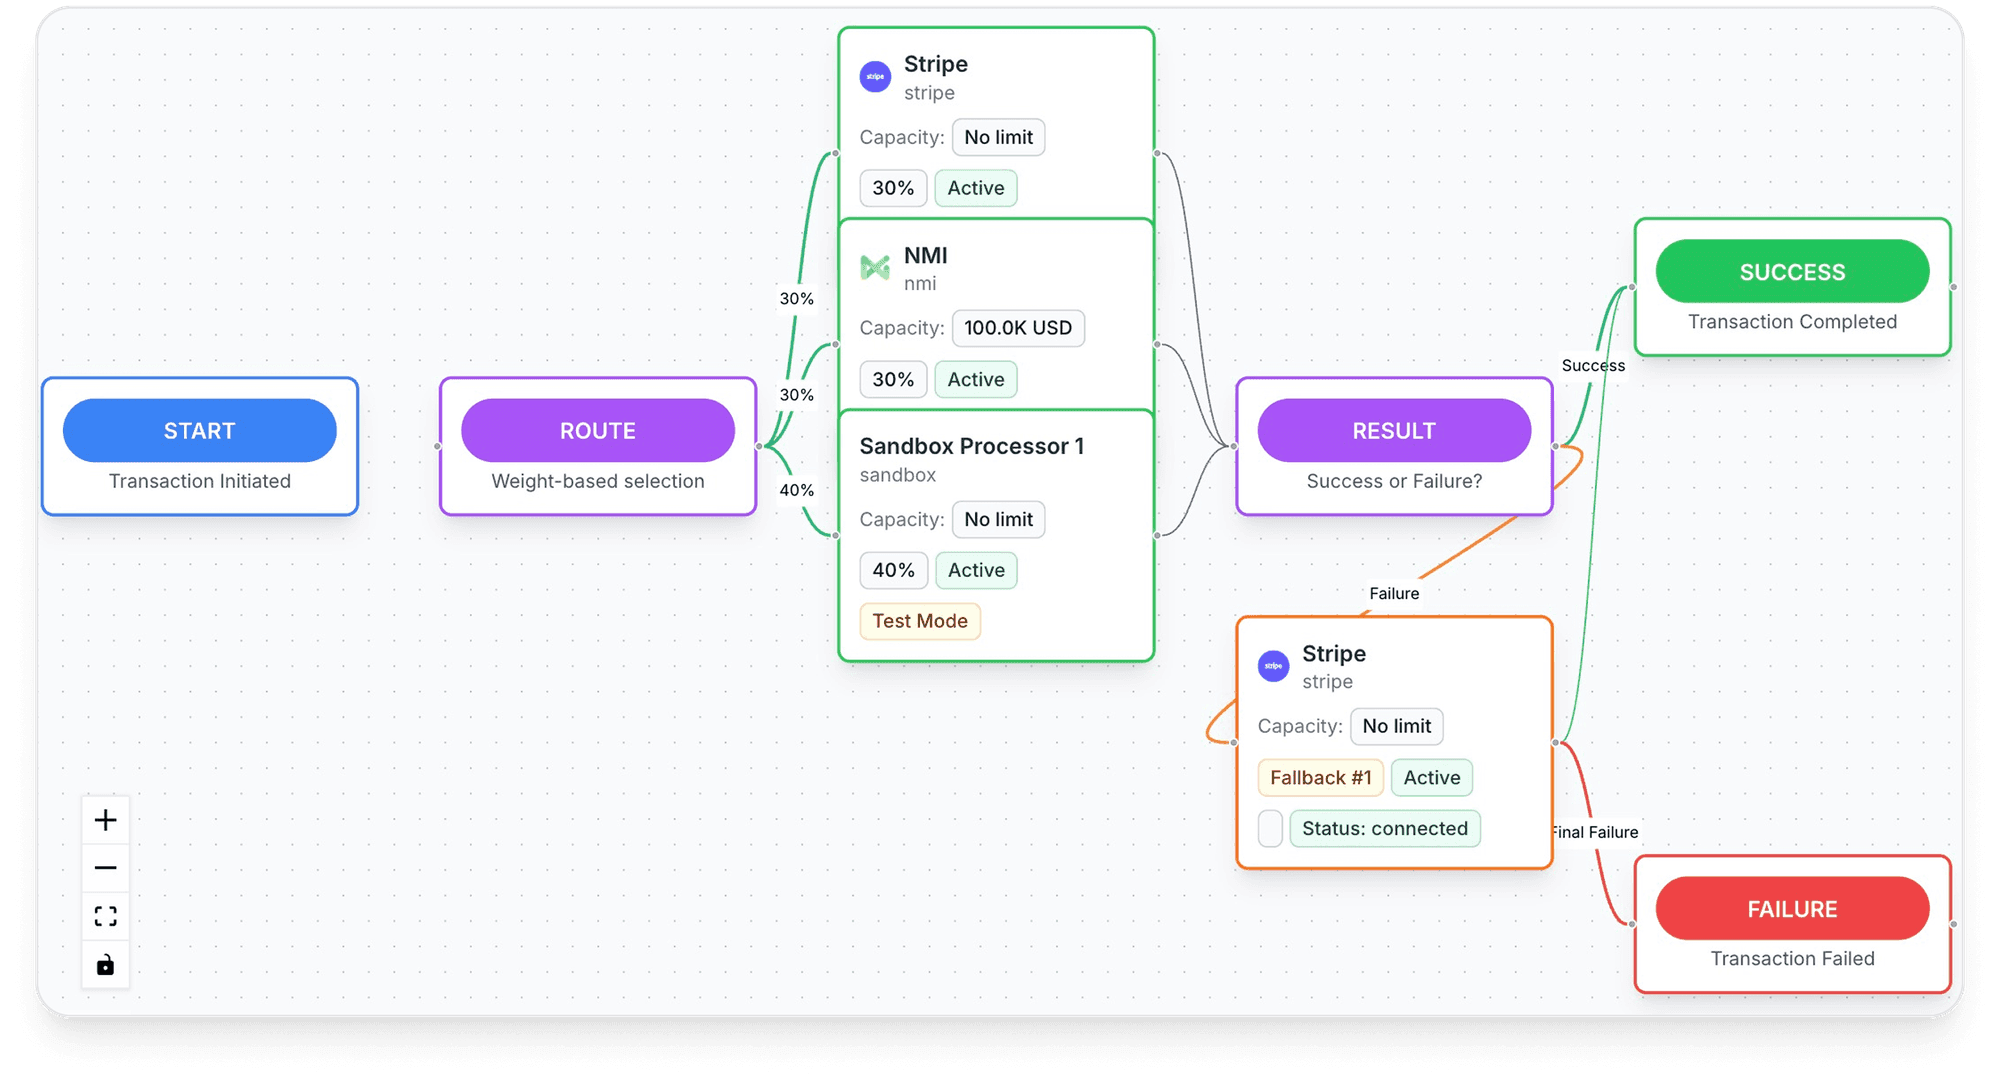
Inside Tagada
See every payment's route, processor by processor
Set the order your processors are tried in, per store, per country or per product.
CAVV vs CVV2 vs AAV vs ECI
These four are often confused because they all appear in the same payment.
| CAVV | CVV2 | AAV (UCAF) | ECI | |
|---|---|---|---|---|
| Network | Visa | All card brands (Visa's term) | Mastercard | All networks, values differ |
| Created by | Issuer ACS, or Visa for attempts | Printed on the card | Issuer ACS plus Mastercard | 3DS result |
| Changes per payment | Unique to each payment | Fixed per card (dCVV2 can change) | Unique to each payment | Set by the outcome |
| What it proves | Cardholder passed 3-D Secure | Customer has the card details | Cardholder passed Identity Check | How the payment was authenticated |
| Where it travels | Authorization request | Authorization request | DE 48, subelement 43 | Authorization and clearing |
| Store after authorization? | ProhibitedBy Visa | ProhibitedBy Visa | Check your processor's rules | Allowed |
Sources: Visa Core Rules, April 2026, sections 1.9.4.1, 5.8.4.4 and 10.15.2.3, and the CVV2 definition;1Visa Core Rules and Visa Product and Service Rules, April 18, 2026 Mastercard Identity Check Program Guide, p. 50 and 105.2Mastercard Identity Check Program Guide, November 19, 2019
Verdict
CVV2 says "I have the card details." CAVV says "the bank checked it was me, for this payment." ECI says which of those happened.
On Mastercard, the issuer's ACS generates a cryptogram and Mastercard completes it to form the AAV. UCAF stands for Universal Cardholder Authentication Field, the place it travels. Mastercard keeps an AAV valid for 10 to 90 days, and its on-behalf validation compares the card number, AAV, DS transaction ID and amount between authentication and authorization.2Mastercard Identity Check Program Guide, November 19, 2019
CAVV result codes: what "invalid CAVV" means
After the issuer checks the CAVV, the authorization response carries a one-character CAVV result. Codes come from Visa; the exact wording and field name depend on your processor. Cybersource returns them in auth_cavv_result:6Cybersource (Visa Acceptance Solutions), Visa Secure response codes
- 2CAVV passed validation and authenticationNothing. Keep the 3DS transaction ID and ECI
- 3, 8 or ACAVV passed validation of an attemptNothing. ECI 6 rules apply
- 6Not validated: the issuer doesn't take partVisa assumes an unverified CAVV is valid
- BPassed, for information only, no liability shiftTreat the payment as unprotected
- 0 or INot validated: data erroneous, or security data invalidCheck field mapping and Base64 encoding
- 1, 4, 7 or 9CAVV failed validationDon't retry with the same CAVV. Run 3-D Secure again
The usual causes of an invalid CAVV are concrete:
- Wrong field or encoding. A CAVV sent as hex, truncated, or put in the wrong field. Stripe asks for the Base64 version that most 3DS providers return.3Stripe API reference, Create a PaymentIntent (three_d_secure)
- Reuse. Visa lets an issuer file a compliance case when an acquirer reuses a validated CAVV on a later ECI 5 transaction with different data, such as another date or amount, and the cardholder denies it.1Visa Core Rules and Visa Product and Service Rules, April 18, 2026
- Changed payment. A different amount or card between authentication and authorization.
- Another processor. Adyen states that you cannot reuse authentication data across PSPs.5Adyen Docs, Standalone 3D Secure authentication
What CAVV changes for an online merchant
Liability shift. Visa's rules make a 10.4 fraud dispute invalid in two cases: ECI 5 with a CAVV from an authentication confirmation, or ECI 6 with a CAVV from an attempt response, except on non-reloadable prepaid cards.1Visa Core Rules and Visa Product and Service Rules, April 18, 2026 It covers fraud claims only. "Not received" or "not as described" disputes still apply. See liability shift.
Clean indicators. An acquirer may put ECI 5 or 6 in the clearing record only if the authorization request included the CAVV.1Visa Core Rules and Visa Product and Service Rules, April 18, 2026 Sending ECI 5 without a CAVV is not a shortcut.
Data handling. Don't store the CAVV after authorization, like CVV2.1Visa Core Rules and Visa Product and Service Rules, April 18, 2026 Keep the transaction ID, ECI and result for your records.
How Tagada helps
3-D Secure inside the checkout
TagadaPay runs native 3DS2, with device intelligence and a rules engine, in the checkout. Payments route across TagadaPay and processors such as Stripe, NMI and Airwallex with one logic, with a cascade to another processor when one is down or times out. Each processor still checks the authentication data it receives, so a CAVV is used for the payment it was created for. Tagada follows Visa and Mastercard rules and the laws that apply to payments.
Frequently asked questions
What is the full form of CAVV?
What is the difference between CAVV and CVV?
What does invalid CAVV or bad CAVV mean?
Can you decode a CAVV?
Is CAVV the same as AAV or UCAF?
Should merchants store the CAVV?
Sources
Checked October 15, 2026- Visa Core Rules and Visa Product and Service Rules, April 18, 2026
- Mastercard Identity Check Program Guide, November 19, 2019
- Stripe API reference, Create a PaymentIntent (three_d_secure)
- Stripe Docs, Import 3D Secure results
- Adyen Docs, Standalone 3D Secure authentication
- Cybersource (Visa Acceptance Solutions), Visa Secure response codes
TagadaPay
Run 3-D Secure and route payments from one checkout
Tell us what you sell and how you sell it. Each application is underwritten, and approval is not guaranteed.
- 01Tell us what you sell and how
- 02Underwriting reviews your business
- 03Process through TagadaPay alongside your other processors