Hosted Payment Gateways: Redirect, Iframe or Your Own Form
How a hosted payment gateway works, what the shopper sees, how far you can brand it, and when it keeps you in SAQ A, with the 2025 script rule.
Article summary
TL;DR
A hosted payment gateway collects the card on a page or form served by the payment provider, not by your site. The shopper is redirected to that page or sees it in an iframe, and you get back a result, never the card number. Done right, it keeps most stores in PCI DSS SAQ A, the shortest questionnaire.
- Three models: a hosted page (redirect), hosted fields (provider iframes inside your page), or your own form sending cards through your systems.
- SAQ A requires every element of the payment page to come from a PCI DSS compliant provider. Nothing on it can come from your site.
- Since April 1, 2025, a store that embeds the provider's form in an iframe must also confirm its page isn't open to script attacks. A full redirect is exempt.
- Branding is the price: logo, colors, font and button style, rarely more. Stripe lets you put its page on your own subdomain as a paid feature.
- The return to your site isn't proof of payment. Confirm each order from the provider's webhook.
 ChatGPT
 Claude
 Perplexity
 Grok
On this page
A hosted payment gateway takes the card on the provider's page, not yours. You give up most of the design of the payment step, and in exchange your systems never touch a card number, which keeps most stores in PCI DSS's shortest questionnaire. This guide covers the three ways to collect a card, what the shopper sees with each, what the PCI SSC actually requires since 2025, and when a hosted page is the right call.
What is a hosted payment gateway?
A hosted payment gateway serves the payment form from the provider's own servers. The shopper fills the cart on your site, then types the card on a page or in a frame that belongs to the provider. The provider runs the authorization and sends you the outcome. You keep a reference, the card brand and the last four digits, which are outside PCI DSS scope; the full number never reaches you.7Stripe Docs, Integration security guide
Adyen's Hosted Checkout is a clean example of the flow:8Adyen Docs, Hosted Checkout
- Your server opens a payment session. It sends the amount, currency, country and your order reference, and gets back the URL of the hosted page.
- You redirect the shopper. The hosted page lists the payment methods available for that amount and country.
- The shopper pays on the provider's page. If a payment fails, the shopper comes back to the same page to try again. By default the page expires one hour after it's created.
- The shopper comes back to your return URL, with the session ID and a result appended to it.
- A webhook confirms the outcome. Adyen sends one per payment attempt; you match it to your order reference and update the order.
Adyen Hosted Checkout. Stripe Checkout and Authorize.net Accept Hosted follow the same pattern with different names.
The same idea goes by several names: hosted payment page, hosted checkout, HPP, or "offsite" payments. Our glossary has a short definition of a hosted payment page. For where the gateway sits next to the processor and the acquirer, see payment gateway vs payment processor.
Hosted page, hosted fields or your own form
"Hosted" covers two different things, and the difference matters for both design and PCI scope. The real question is who serves the payment form.
| Model | Where the card is typed | What you design | Usual questionnaire |
|---|---|---|---|
| Hosted payment page (redirect) | A full page on the provider's domain | Logo, colors, font, sometimes a subdomain | SAQ A1PCI Security Standards Council, FAQ: If all elements of payment pages originate from a PCI DSS compliant service provider, is the merchant eligible for SAQ A or SAQ A-EP?2PCI Security Standards Council blog, FAQ clarifies new SAQ A eligibility criteria for e-commerce merchants, February 28, 2025 |
| Hosted page embedded in an iframe | The provider's page, framed inside yours | Your page around it; the frame follows the provider's settings | SAQ A, plus the 2025 script criterion2PCI Security Standards Council blog, FAQ clarifies new SAQ A eligibility criteria for e-commerce merchants, February 28, 2025 |
| Hosted fields | Separate provider iframes for card number, expiry, CVV, inside your own form | The whole form layout and its styling | SAQ A or A-EP, depending on the provider's setup and your acquirer10PayPal Developer, Card fields (JavaScript SDK v6)11Braintree Developer Docs, Hosted Fields overview |
| Your own form, card sent by your page's JavaScript or direct post | Fields served by your site | Everything | SAQ A-EP3PCI Security Standards Council, Self-Assessment Questionnaire A-EP for PCI DSS v4.0, April 2022 |
| Card reaches your servers | Your form, your backend | Everything | Beyond A-EP, usually SAQ D3PCI Security Standards Council, Self-Assessment Questionnaire A-EP for PCI DSS v4.0, April 2022 |
Stripe's three Checkout options show the range inside one provider. The full page can be a redirect to a Stripe-hosted page or embedded on your site, with 15 configurable settings in brand settings. The embedded form offers 70 settings through its Appearance API. Elements gives full CSS control, and Stripe rates it the most work to build and maintain.4Stripe Docs, Build a payments page (Checkout)
The integration side, APIs, SDKs, webhooks and testing, is covered in our guide on how to integrate a payment gateway.
What the shopper sees
Full redirect
- Your cartShopper clicks Pay
- redirect
 Provider's pageDifferent URL, your logo and colors
- back toYour confirmation pageReturn URL with a result
Fastest to ship, the shopper sees another domain
Embedded form or hosted fields
- Your checkout pageYour layout, your order summary
- inside
 Provider's iframeCard typed inside the frame
- Same pageResult shown without leaving
Shopper stays on your URL, more front-end work and a script check
With a redirect, three things change for the shopper:
- The address bar. The payment happens on the provider's domain. Stripe lets you serve its hosted page on a subdomain of yours, such as
payments.example.com, as a paid feature, one custom domain per account. It works only with server-side redirects.6Stripe Docs, Use your custom domain - The look. You set the branding the provider allows, nothing more (see below).
- The name. The page shows your business name. Stripe reminds merchants that network rules generally require an accurate, consistent business name and logo, and that a name customers don't recognize adds to confusion and chargebacks.5Stripe Docs, Customize appearance: full hosted page
What you can change on each provider's page, as documented:
| Provider | What you can set on the hosted page |
|---|---|
| Stripe Checkout, hosted page | Logo or icon, background color, button color, font, shapes, display name; custom subdomain as a paid add-on5Stripe Docs, Customize appearance: full hosted page6Stripe Docs, Use your custom domain |
| Adyen Hosted Checkout | A theme with a brand logo and a display name shown to the shopper; payment methods follow amount and country8Adyen Docs, Hosted Checkout |
| Authorize.net Accept Hosted | Accent color, button text, which payment options show (card, eCheck, saved profiles), address and email fields, receipt and return URLs, CAPTCHA9Authorize.net Developer Center, Accept Hosted |
Does a hosted page cost conversions?
Every provider guide in the search results says a redirect "may" raise cart abandonment. None of them publishes a measured figure, and neither do we. What you can say for sure is where the friction and the trust come from.
Where a hosted page helps
- A page the shopper already knows can reassure: a familiar provider, wallets like Apple Pay and Google Pay already built in.
- Payment methods and local options come with the provider. Stripe's hosted page includes subscriptions, tax, promo codes, upsells and cross-sells in its order summary.4Stripe Docs, Build a payments page (Checkout)
- Provider updates (new methods, 3D Secure changes) reach your checkout without a release on your side.
- Less to build: a session call, a redirect, a webhook.
Where it costs you
- A change of domain and design at the moment of paying.
- You can't A/B test the payment step the way you test your cart, beyond the settings the provider exposes.
- Your analytics lose the shopper for a few steps; cross-domain tracking has to be set up on purpose.
- The order summary, upsells and fields you can show are the provider's, not yours.
If your checkout is a lever you test every week, measure it: run the hosted page and an embedded form against the same traffic before deciding. Our guide to checkout flow covers what to test in the steps before payment.
Does a hosted payment gateway take you out of PCI scope?
Not out of it. It moves most of the work to the provider. You still validate compliance once a year, usually with the self-assessment questionnaire (SAQ) your acquirer asks for. Stripe, for example, is assessed as a PCI Level 1 service provider and still asks every business to attest its own compliance each year.7Stripe Docs, Integration security guide
What a hosted gateway changes is which questionnaire you file. The PCI Security Standards Council draws the line on where each element of the payment page comes from:
To be eligible for SAQ A, all elements of the payment pages must only originate from PCI DSS compliant service provider(s), and no single element of a payment page can originate from the merchant's website.
For SAQ A-EP, each element must come either from your website or from a PCI DSS compliant provider. If any element comes from a third source, neither questionnaire applies, and every other eligibility criterion has to be met too.1PCI Security Standards Council, FAQ: If all elements of payment pages originate from a PCI DSS compliant service provider, is the merchant eligible for SAQ A or SAQ A-EP? SAQ A-EP covers stores whose site doesn't receive card data but affects the security of the payment; it still requires that you don't store, process or transmit any account data electronically.3PCI Security Standards Council, Self-Assessment Questionnaire A-EP for PCI DSS v4.0, April 2022
Stripe gives the order of magnitude on the other side: a business that takes untokenized card numbers on its own payment page "might be required to meet more than 300 security controls in PCI DSS".7Stripe Docs, Integration security guide
Who decides your SAQ
Your acquirer, or the card brands, decide which questionnaire you file. The PCI SSC tells merchants to check with their acquirer that SAQ A fits their setup.2PCI Security Standards Council blog, FAQ clarifies new SAQ A eligibility criteria for e-commerce merchants, February 28, 2025 Provider labels differ too: Authorize.net describes Accept Hosted as keeping "SAQ-A level PCI compliance", while PayPal's card fields guide lists "PCI DSS SAQ A-EP considerations".9Authorize.net Developer Center, Accept Hosted10PayPal Developer, Card fields (JavaScript SDK v6)
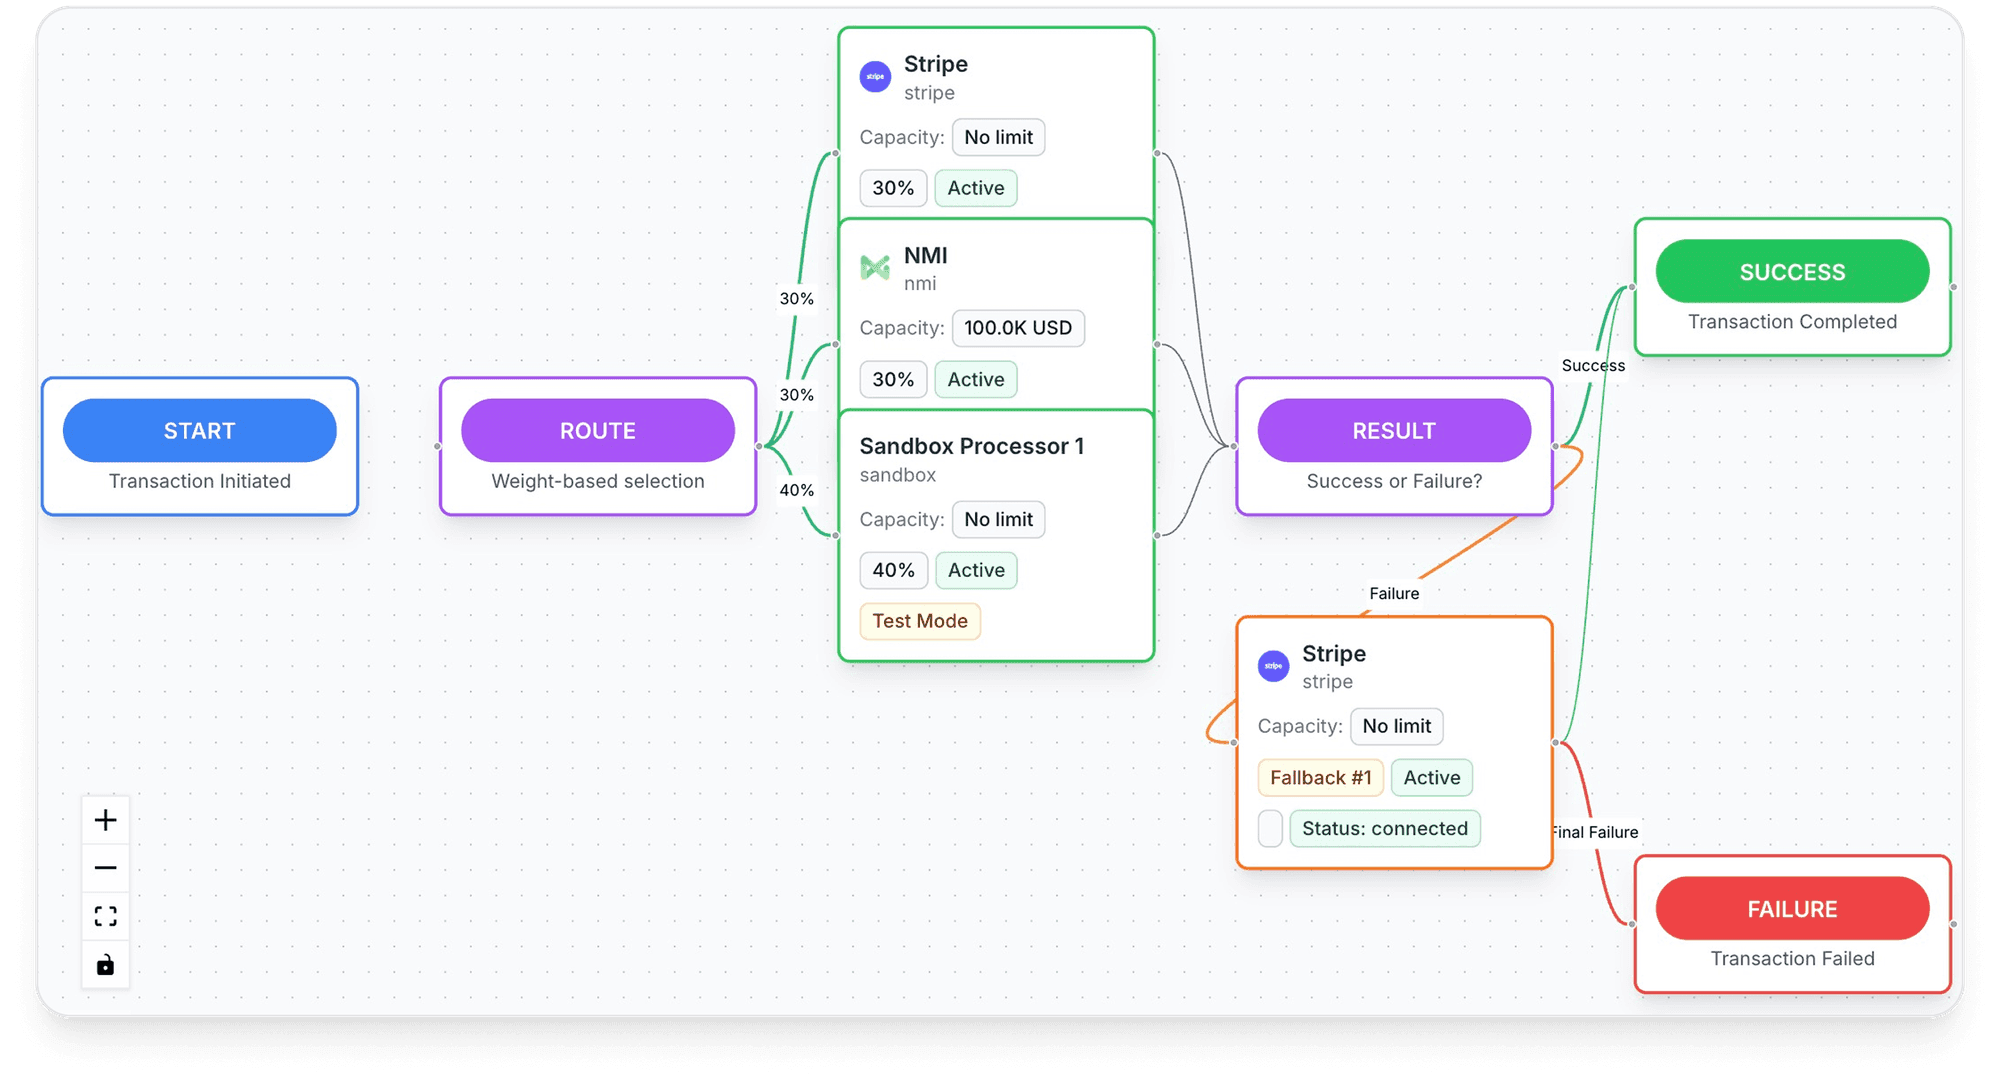
Inside Tagada
See every payment's route, processor by processor
Set the order your processors are tried in, per store, per country or per product.
The 2025 SAQ A script rule
Since April 1, 2025, SAQ A under PCI DSS v4.0.1 has a new eligibility criterion: the merchant has confirmed that its site "is not susceptible to attacks from scripts that could affect the merchant's e-commerce system(s)".2PCI Security Standards Council blog, FAQ clarifies new SAQ A eligibility criteria for e-commerce merchants, February 28, 2025 The target is the skimming script that sits on the page around the payment form and copies what the shopper types, a web version of card skimming.
- Full redirect to the provider's page (HTTP 30x, meta or JavaScript redirect)NoFile SAQ A if your acquirer agrees. Still keep the page that redirects clean
- Payment link sent by email, payments fully outsourcedNoSAQ A if the other criteria are met
- Provider's form embedded in an iframe on your pageYesConfirm your page isn't susceptible to script attacks, one of the two ways below
- Your page's JavaScript collects or sends the cardNot SAQ A at allSAQ A-EP, with its full set of requirements
The Council accepts two ways to confirm an embedded form is protected:2PCI Security Standards Council blog, FAQ clarifies new SAQ A eligibility criteria for e-commerce merchants, February 28, 2025
Protect the page yourself
Apply protections against scripts that target account data, such as those in PCI DSS requirements 6.4.3 (an inventory and authorization of payment page scripts) and 11.6.1 (change and tamper detection). You or a third party can run them.
Get it from your provider
Get written confirmation from your PCI DSS compliant provider that its solution, implemented as instructed, protects the payment page against script attacks. Ask for it before you pick a provider.
The scope logic behind tokens and encryption is in tokenization vs encryption, and the provider-side checks in our guide to PCI compliant payment gateways.
Four hosted options from official docs
| Option | How it's shown | What the docs say about scope | Detail worth knowing |
|---|---|---|---|
| Stripe Checkout | Redirect to a Stripe-hosted page, or embedded on your site | Card data goes to Stripe without passing through your servers, "reducing your PCI obligations"7Stripe Docs, Integration security guide | Hosted page recommended by Stripe as the lowest-maintenance option4Stripe Docs, Build a payments page (Checkout) |
| Adyen Hosted Checkout | Redirect to an Adyen-hosted page | The Hosted Checkout page itself makes no SAQ statement; check Adyen's PCI guide and your acquirer | Don't put names or emails in the return URL: Adyen forbids personal data there8Adyen Docs, Hosted Checkout |
| Authorize.net Accept Hosted | Full-page redirect, lightbox, or iframe in your page | "SAQ-A level PCI compliance"9Authorize.net Developer Center, Accept Hosted | The form token is valid for 15 minutes; fields marked required must also be set in the Merchant Interface9Authorize.net Developer Center, Accept Hosted |
| PayPal card fields / Braintree Hosted Fields | Provider iframes for card number, CVV, expiry, postal code inside your form | Braintree: built for "SAQ A eligibility"; PayPal v6 card fields: "SAQ A-EP considerations"10PayPal Developer, Card fields (JavaScript SDK v6)11Braintree Developer Docs, Hosted Fields overview | Hosted fields, not a hosted page: you design the form around them |
When to choose a hosted payment page
Short version
Choose a hosted page when getting card payments live with the least PCI work matters more than designing the payment step. Choose hosted fields or an embedded form when checkout is a conversion lever you test, and accept the 2025 script check. Build your own card form only if you're ready for SAQ A-EP or more.
A hosted page usually fits when:
- You're launching, or your team has no one to own PCI DSS controls on a payment page.
- You sell one-off orders and your payment step rarely changes.
- You want the provider's wallets and local methods without building them.
- You use payment links, invoices or emails as a sales channel anyway.
Move to hosted fields or an embedded form when:
- You test checkout layouts, order bumps or copy, and the payment step is part of that test.
- Shoppers drop at the handoff and you've confirmed it with your own data.
- You need your order summary, your fields and your upsells on the same page as the card.
What stays your job
The redirect isn't the receipt
A shopper landing on your success URL doesn't prove the payment went through. Adyen says the session status returned there doesn't update and sends a webhook for each attempt; fulfill orders from the webhook.8Adyen Docs, Hosted Checkout Stripe tells you to verify webhook signatures and serve your webhook endpoint over TLS.7Stripe Docs, Integration security guide
- The page before the payment. Scripts on your cart page run in the shopper's browser just before the handoff. Stripe advises keeping third-party JavaScript on payment pages to a minimum.7Stripe Docs, Integration security guide
- TLS everywhere. Payment pages and every resource they load must use TLS 1.2 or above, according to Stripe's security guide.7Stripe Docs, Integration security guide
- Your annual attestation, whatever the provider promises.
- Tracking across domains, so ad platforms still see the purchase. See cross-domain tracking.
- Disputes and refunds. The hosted page takes the card; the chargebacks still come to you. Our guide to chargeback prevention covers the rest.
Where Tagada fits
How Tagada helps
Your checkout, several processors behind it
Tagada's checkout carries one-click upsells, order bumps, A/B tests, Apple Pay and Google Pay, and payments route across TagadaPay and processors such as Stripe, NMI and Airwallex, with one logic and a cascade to another processor when one is down or times out. The card vault lets you switch processors without re-onboarding customers, and running subscriptions keep charging. 3D Secure 2 is native, alongside device intelligence and a rules engine. Pricing is on the pricing page.
Whatever you choose, ask any provider the same three questions: who serves the payment form, which SAQ your acquirer will accept for that setup, and whether the provider gives written confirmation for the 2025 script criterion.
Frequently asked questions
What is a hosted payment gateway?
What is the difference between a hosted and a non-hosted payment gateway?
Does a hosted payment page make me PCI compliant?
Are hosted payment pages safe for customers?
Can I customize a hosted payment page?
Is an iframe checkout a hosted payment page?
Sources
Checked October 14, 2026- PCI Security Standards Council, FAQ: If all elements of payment pages originate from a PCI DSS compliant service provider, is the merchant eligible for SAQ A or SAQ A-EP?
- PCI Security Standards Council blog, FAQ clarifies new SAQ A eligibility criteria for e-commerce merchants, February 28, 2025
- PCI Security Standards Council, Self-Assessment Questionnaire A-EP for PCI DSS v4.0, April 2022
- Stripe Docs, Build a payments page (Checkout)
- Stripe Docs, Customize appearance: full hosted page
- Stripe Docs, Use your custom domain
- Stripe Docs, Integration security guide
- Adyen Docs, Hosted Checkout
- Authorize.net Developer Center, Accept Hosted
- PayPal Developer, Card fields (JavaScript SDK v6)
- Braintree Developer Docs, Hosted Fields overview
TagadaPay
Keep checkout yours, route payments across processors
Tell us what you sell and how you sell it. Each application is underwritten, and approval is not guaranteed.
- 01Tell us what you sell and how
- 02Underwriting reviews your business
- 03Process through TagadaPay alongside your other processors